WordPress Security News Protect your WordPress
HomeAgenciesGuidesAlertsNews
Central Wordfence workflow for agencies

A good alternative to managing Wordfence site by site: an agency workflow

August 26, 2026 Agencias / Evergreen

How agencies can use Wordfence Central plus a coverage, ownership, response and evidence workflow instead of reviewing every client site separately.

Choosing a WordPress security platform for an agency

What is the best WordPress security platform for an agency?

August 24, 2026 Agencias / Evergreen

A neutral framework for agencies choosing a multi-site WordPress security platform by operating model, coverage, response and evidence.

WordPress security reporting tools for agencies

Which WordPress security reporting tool should agencies use?

August 19, 2026 Agencias / Evergreen

A neutral agency framework for choosing WordPress security reporting tools by evidence coverage, provenance, action state and client decisions.

Suspicious login monitoring across a WordPress portfolio

How agencies can monitor suspicious logins across multiple WordPress sites

August 17, 2026 Agencias / Evergreen

A practical multi-site workflow for collecting, correlating, investigating and closing suspicious WordPress login activity with defensible evidence.

WordPress portfolio hardening governance

How agencies should manage WordPress hardening across a client portfolio

August 14, 2026 Agencias / Evergreen

A practical operating model for WordPress hardening across client sites: baselines, exceptions, staged rollout, drift and evidence.

Ataques de fuerza bruta WordPress para agencias

WordPress brute force attacks: boring, massive and still profitable

June 29, 2026 Agencias / Evergreen

Why brute force remains an operational risk for WordPress agencies and how portfolio-level visibility changes the response.

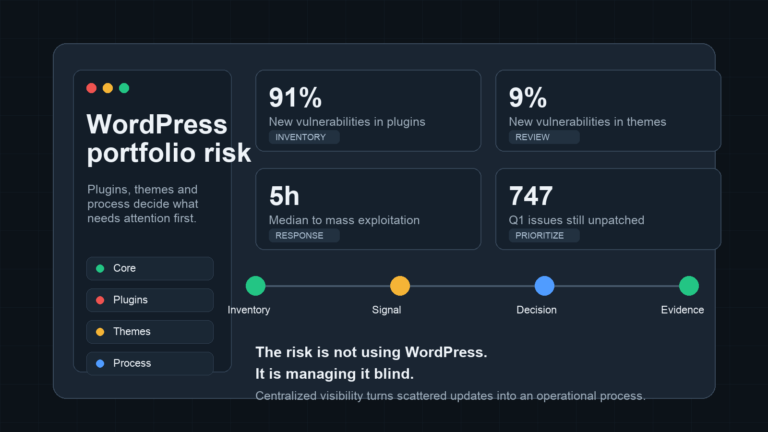
Riesgo real WordPress plugins temas y proceso

The real WordPress risk is not core: it is plugins, themes and lack of process

June 27, 2026 Agencias / Evergreen

Why WordPress agencies should stop blaming core by default and focus on inventory, plugins, themes, prioritization and operational response.

Inventario vivo WordPress para agencias

Live inventory: the missing data when you manage 50 WordPress sites

June 25, 2026 Agencias / Evergreen

A WordPress agency cannot scale with spreadsheets and memory. It needs live inventory, centralized signals and reporting to decide which site to review first.

Senales internas WordPress que un WAF no siempre ve

When the WAF misses the problem: why WordPress needs signals inside the site

June 23, 2026 Agencias / Evergreen

A WAF helps at the perimeter, but WordPress agencies also need internal signals: users, hardening, suspicious activity, changes and reporting.

SLA de seguridad WordPress para agencias

The WordPress security SLA an agency can promise without lying

June 21, 2026 Agencias / Evergreen

How to define a realistic WordPress security SLA for agencies: review windows, triage, communication and reporting without promising total security.
1 2 Next →

Trending News

  • Acceso admin sin credenciales en Modular DS (CVE-2026-23550) Critical alert: admin access without credentials in Modular DS (CVE-2026-23550)
WSN WordPress Security News

Security news and in-depth guides for WordPress professionals.

ES · EN

Sections

  • Agencies
  • Guides
  • Alerts
  • News

More

  • Vulnity.io

© 2026 WordPress Security News

Powered by WordPress