A good alternative to managing Wordfence site by site: an agency workflow
How agencies can use Wordfence Central plus a coverage, ownership, response and evidence workflow instead of reviewing every client site separately.
Section: Agencias
How agencies can use Wordfence Central plus a coverage, ownership, response and evidence workflow instead of reviewing every client site separately.
A neutral framework for agencies choosing a multi-site WordPress security platform by operating model, coverage, response and evidence.
A neutral agency framework for choosing WordPress security reporting tools by evidence coverage, provenance, action state and client decisions.
A practical multi-site workflow for collecting, correlating, investigating and closing suspicious WordPress login activity with defensible evidence.
A practical operating model for WordPress hardening across client sites: baselines, exceptions, staged rollout, drift and evidence.
Why brute force remains an operational risk for WordPress agencies and how portfolio-level visibility changes the response.
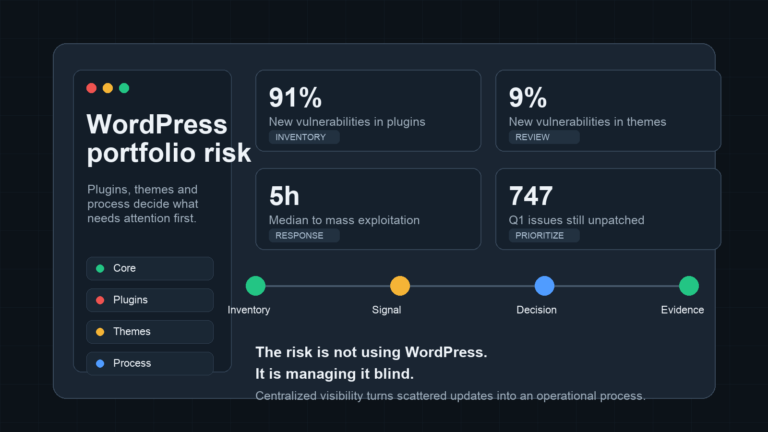
Why WordPress agencies should stop blaming core by default and focus on inventory, plugins, themes, prioritization and operational response.
A WordPress agency cannot scale with spreadsheets and memory. It needs live inventory, centralized signals and reporting to decide which site to review first.
A WAF helps at the perimeter, but WordPress agencies also need internal signals: users, hardening, suspicious activity, changes and reporting.
How to define a realistic WordPress security SLA for agencies: review windows, triage, communication and reporting without promising total security.